

Direct debits and standing orders automate instructions created by humans, however, agentic payments are different: that is, software may search for suppliers, compare terms, negotiate within a mandate and initiate settlement without a person approving every step. This shift does not make banks, cards or lawyers obsolete - it changes the question from, “can the payment be processed?” to, “can every participant prove who is acting, under what authority, on which terms, and with what recourse if something fails?”
The UK’s authorised push payment regime illustrates why this matters. Since October 2024, qualifying victims of APP scams using faster payments can generally expect reimbursement within five business days, subject to the rules, exceptions, plus an £85,000 maximum. Under the regime, sending and receiving payment service providers typically share liability on a 50:50 basis where a scam payment qualifies. The policy gives payment firms stronger incentives to prevent fraud, but it also means banks must scrutinise payment instructions closely. Therefore, digital wallets should not be presented as a way to evade those protections. A more useful question is whether a different settlement architecture can verify identity, authority and contractual conditions before value moves. In practice, that scrutiny is making even legitimate high value purchases harder. Buying a car with cleared funds is no longer always straightforward: banks may delay or block transfers that look unusual, and a claim that the vehicle is being bought from a friend or family member can be treated as a fraud indicator when the facts do not match. Hence, where a payment is later found to be a scam, the issuing and receiving banks may each carry 50% of the reimbursement liability. Public discussion of these frictions, including cases of banks stopping customers from completing large cash purchases, has become more visible see - for example, coverage of bank intervention on car purchases.
A wallet should be more than a key store
Enterprise digital-asset infrastructure already shows what “correctly structured” can mean. Fireblocks, for example, allow organisations to apply transaction rules based on destination, asset, amount, jurisdiction and approval thresholds, with multi-party approvals and audit trails. Moreover, the lesson is broader than crypto custody: a wallet used by an AI agent can act as a control plane that determines what the agent may do before any signature releases value. That model becomes more relevant as agentic-commerce standards mature, such as:
· Visa’s Trusted Agent Protocol - uses cryptographic signatures to help merchants distinguish approved AI agents from malicious bots and validate the agent’s stated intent.
· Google’s Agent Payments Protocol (AP2) - uses cryptographically signed “mandates” to record what a user authorised, including price limits and other conditions.
· Mastercard’s Verifiable Intent - similarly aims to create tamper-resistant evidence of what a consumer instructed an agent to do.
· OpenAI’s Agentic Commerce Protocol - developed with Stripe, keeps merchants in control of payment processing and requires explicit user confirmation in its initial checkout model.
Certainly, live deployments are beginning to test these ideas: Santander and Mastercard completed a live end-to-end AI-agent payment in a regulated banking framework in March 2026, using predefined permissions and limits; Worldline, ING and Mastercard later completed a production agentic payment in Europe. However, although these examples do not prove that one architecture will dominate, they do demonstrate that identity, permissioning and accountability are already becoming design requirements rather than theoretical concerns. Given there is a need for a digital enabled wallet to handle digital assets, then surely there is a need for a digital wallet to handle both your digital identity and that of the agentic agents which are acting on your behalf and also other agentic agents that want to engage with you/your agentic agent?
Case study: checkout is becoming an identity problem
Visa introduced Trusted Agent Protocol after reporting a sharp rise in AI-driven traffic to US retail sites. The problem for merchants was not simply payment acceptance: automated traffic could represent a legitimate shopping agent, a scraper or a malicious bot. Visa’s response has been agent-specific cryptographic recognition designed to be checked during the interaction. For a higher-value transaction, however, proving that an agent is legitimate may not be enough. A company buying £250,000 of equipment may also need to know whether the agent has authority to bind the buyer, whether the supplier exists, whether sanctions and KYC checks have been completed, whether delivery terms are enforceable and whether funds should be released immediately or only after inspection. This is where a governed wallet can extend beyond checkout.
Insurance can help to minimise residual risk, not replace verification
No identity system is infallible, hence there is always some residual risk. Credentials can be stolen, software can be compromised and an authorised agent can still act incorrectly. Munich Re identifies agentic AI, prompt injection, synthetic identities and technology errors as emerging cyber exposures, whilst Marsh reports growing demand from financial institutions for customised insurance addressing AI, cyber and operational risks. Therefore, although insurance has a potentially important role, the sequencing matters. Insurance should not be treated as proof that an agent is genuine. Instead, a wallet could be designed so that, where suitable cover is available, insurance backs the residual risk after identity, mandate and transaction controls have passed. Possible cover could respond to defined losses caused by identity-assurance failure, credential compromise, unauthorised execution, cyber events or settlement failure. In addition, underwriters would be expected to require evidence of controls - e.g. strong authentication, limited mandates, transaction logs, revocation, approval thresholds and clear responsibility. In this model, better technology is able to make risk more measurable and potentially more insurable; insurance provides capital-backed recourse when prevention fails. Furthermore, as we see more and more agentic commerce, there will surely be a growing need to know your agent (KYA) solutions. That is to say, who is the agentic agent acting on behalf of, is the agentic agent real or fake and what insurance can one purchase to mitigate the risk of you or your agent being duped?
Why a lawyer may need to remain “in the loop”
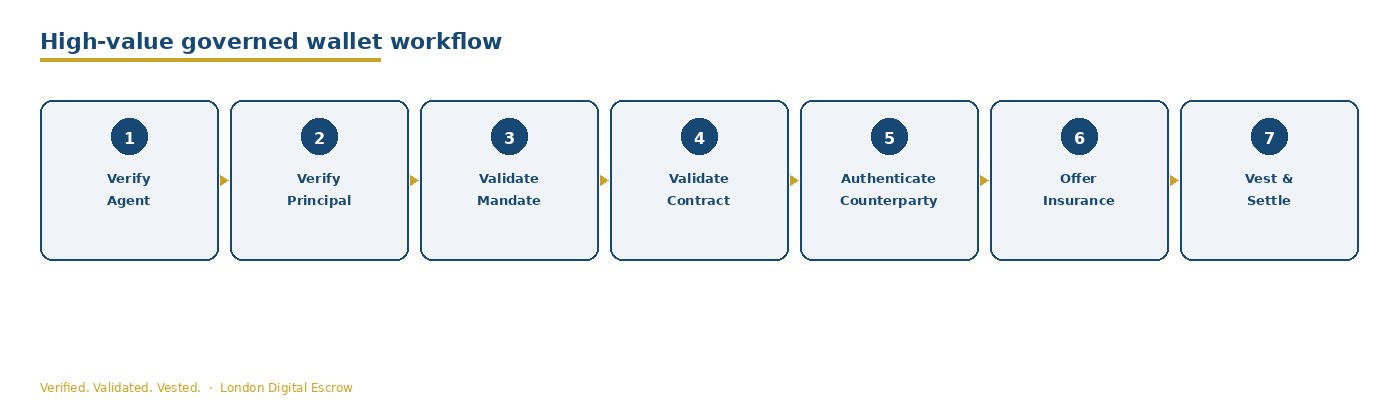
For routine low-value purchases, adding a lawyer would be disproportionate. For property, M&A, large procurement, escrow-style transactions or cross-border deals, then human legal validation may be valuable precisely because the transaction is complex or difficult to reverse. The Law Commission has concluded that English law can accommodate smart legal contracts, but that does not mean code automatically creates legal certainty. Parties still need clarity over identity, authority, governing law, contractual obligations and remedies. A risk-based wallet could therefore require legal approval above agreed thresholds - e.g. where AYC/AML checks are needed. A solicitor might verify the principals, confirm the agent’s authority, validate the contract between the buyer and the seller and establish the conditions under which value can vest - i.e. payment is made. Marsh’s 2026 analysis of AI-assisted M&A due diligence provides an interesting parallel: W&I insurers generally accept AI-supported due diligence where its use is proportionate, governed and supported by appropriate human oversight.
Source: London Digital Escrow
The precise controls would depend on transaction value, jurisdiction, asset type and regulatory obligations.
What does this mean for APP liability?
There is no reason why, once funds have moved into a correctly structured digital wallet, a wallet-to-wallet commercial transfer may not be the same bank-executed faster payment that triggers the conventional APP reimbursement pathway. This is a useful architectural question, not a settled legal conclusion: the on-ramp and off-ramp remain bank payments, AML, sanctions and other regulatory duties continue to apply, and the precise treatment of hybrid wallet flows requires legal and regulatory analysis. And caution strengthens the educational case for governed wallets - the purpose should not be to remove responsibility, it should be to make identity, authority, contractual intent, evidence and risk allocation visible and machine-readable before settlement. Agentic commerce may create very large transaction volumes, but adoption will depend on trust. Visa, Mastercard, Google and OpenAI are all building identity, mandate and payment-control layers. Institutional wallet providers demonstrate that policy controls can be embedded before execution, insurers are examining AI-related cyber and liability risks, whilst English law can support smart legal contracts.
The unanswered question is how these components will be combined. Could a wallet verify the agent and principal, enforce a transaction-specific mandate, attach a legally validated contract, obtain insurance for residual risk and release value only when agreed conditions are satisfied? If so, the digital wallet evolves from a place that holds keys into a governed transaction environment. For low-value commerce, much of this could be automated. For higher-value transactions, insurance and a lawyer-in-the-loop could provide additional layers of confidence without pretending that technology eliminates risk.